
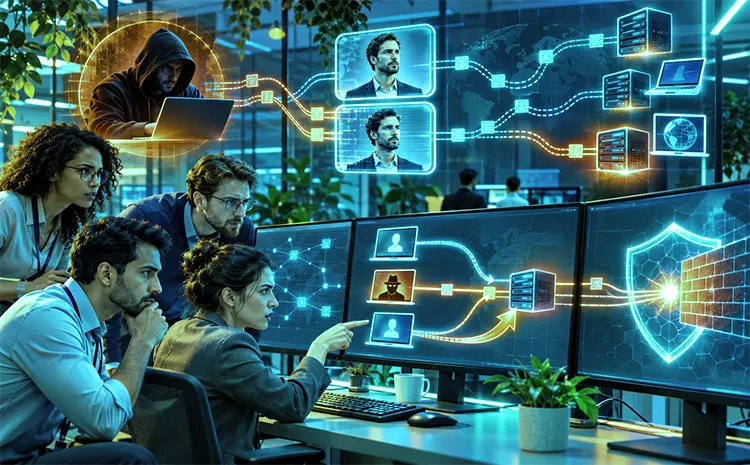
Cybercriminals deliberately use the IP spoofing technique to bypass protection mechanisms and introduce malware. Learn what lies behind it, how dangerous this technology is, and what measures you can take to secure your network.
What Is IP Spoofing?
Spoofing generally describes a technique of concealment or deception in digital systems. This involves manipulating a digital identity – such as an email address, domain, phone number, or IP address – to impersonate a trusted entity. The goal is to gain unauthorized access to systems, steal information, or deliberately trigger malicious behaviour.
IP spoofing is a specific form of this deception at the network level. Unlike email or website spoofing, this manipulation does not affect the browser display or email address but rather the technical origin of data packets within a network – the so-called IP address. Since IP addresses are a central element of computer communication, IP spoofing deliberately abuses trust in existing network structures, with serious consequences for security and stability.
How Attackers Manipulate IP Headers to Conceal Their Identity
Every data packet on the internet contains a so-called IP header. This header is comparable to the sender’s address on a traditional envelope; it indicates where the packet originates (source address) and where it is sent (destination address). In digital communication, this header is essential for correctly routing responses and managing communication processes.
IP spoofing involves deliberately forging the source IP header of a packet. The attacker overwrites the actual source address with an arbitrary one – often a legitimate and trusted IP address. This leads the receiving system to believe it is communicating with a known computer or internal system, even though the request actually originates from an external, malicious source.
This deception is particularly problematic because many systems use IP-based security mechanisms – such as firewalls, access controls, or internal trust models that automatically classify trusted IP addresses as secure. With a forged header, an attacker can circumvent these mechanisms and gain access to systems or confidential data without the victim immediately detecting the fraud.
Also Read: Instructions To Conceal Your IP Address And Peruse Without Being Followed
How Does IP Spoofing Work Technically?
Devices on a network, especially over the internet, use the Internet Protocol (IP) to communicate with each other. Every piece of information transmitted is broken down into smaller units called IP packets. These contain not only the actual user data but also control information in the so-called IP header. The IP header includes, among other things:
- Source IP address – the address of the sending device
- Destination IP address – where the packet is sent
- Protocol information – such as whether it is TCP or UDP.
- Sequence numbers – for packet assignment in TCP
- Further technical details regarding fragmentation, TTL (Time to Live) and checksums
The information in the header is crucial for forwarding and assigning packets. However, this header data is neither encrypted nor verifiable in the IPv4 protocol. This means it can be manipulated with minimal effort – and this is precisely where IP spoofing comes in.
How Attackers Manipulate the Source IP Address
In IP spoofing, an attacker deliberately overwrites the source IP address in the header of an outgoing packet. This makes the packet appear to the target system as if it originated from a legitimate or trusted computer – such as an internal server or a known external service. The goal of this forgery is either:
- To gain unauthorised access,
- To exploit trust relationships between systems,
- or To conceal one’s own identity, for example, in the context of a DDoS attack.
The response packets from the target system are then not sent to the actual attacker but to the spoofed source address. However, this step is irrelevant in many attack scenarios – especially in attacks where no response is expected (e.g., flooding, amplification, one-off connection attempts).
Blind Spoofing vs Non-Blind Spoofing
There are two basic types of IP spoofing attacks, which differ primarily in the attacker’s position within the network:
Blind spoofing: In blind spoofing, the attacker operates from outside the network containing the target and the spoofed source IP address. Since they have no way of viewing the response packets, they must guess TCP sequence numbers to successfully manipulate data or hijack sessions. This used to be relatively straightforward, as many operating systems generated sequence numbers according to a predictable pattern. Today, randomly generated sequence numbers make these attacks considerably more difficult. Nevertheless, older devices or poorly configured systems remain vulnerable to this method.
Non-Blind Spoofing: In non-blind spoofing, the attacker is on the same subnet as the target system – for example, within a local area network (LAN) or a poorly secured WLAN. Since they can directly sniff the network traffic in this case, they don’t need to make any guesses. They can intercept, analyze, and manipulate the actual sequence numbers.
In practice, non-blind spoofing is significantly more effective but also more difficult to implement, as the attacker must have physical or logical access to the same network segment. However, such attacks can certainly occur in corporate networks with inadequate network segmentation or outdated switches – especially if attackers have already gained initial access.
Why Is IP Spoofing Dangerous?
IP spoofing is one of the most subtle yet effective methods in the repertoire of professional cybercriminals. Its danger lies not primarily in its technical complexity but in the insidious simplicity with which it circumvents fundamental security concepts – usually undetected and without leaving any direct traces. This is precisely why it poses a significant risk to companies, especially those with outdated or inadequately protected IT infrastructures.
At its core, IP spoofing pursues one goal: to conceal the attacker’s true identity. When the source address of a data packet is manipulated, it makes the attacks seem to come from trusted or internal sources. This deception undermines key defence mechanisms such as firewalls, access controls, and IP-based trust models, significantly hindering the identification of an attack’s origin. For IT security teams and law enforcement agencies, this presents a major obstacle to analysing and tracking incidents.
How IP Spoofing Can Bypass Common Security Mechanisms
IP spoofing manipulates the source address of a data packet, making it appear to originate from a trusted or internal source. This obfuscation undermines key security mechanisms such as:
- Firewalls with IP filter rules,
- Access controls for specific network areas or services,
- Trust models within internal networks (“trust this IP”),
- or IP whitelisting for remote access.
The problem: These mechanisms rely on the authenticity of the source IP address. IP spoofing completely undermines this trust by impersonating the IP address of a trusted system. This allows attackers to bypass firewall rules or gain access to services that should only be available internally.
This is particularly critical in networks with outdated architecture or insufficient segmentation, where there is no additional authentication at a higher protocol level – such as via certificates or encrypted communication.
Why IP Spoofing Can Go Undetected
Manipulation often goes undetected for a long time.
IP spoofing takes place at a low network layer. The packets appear outwardly legitimate; without in-depth logging or packet analysis, the attack often goes undetected, especially when:
- The response packets will not be analyzed,
- No packet filtering is performed on source addresses.
- or Network monitoring is missing.
Unlike traditional phishing or malware attacks, IP spoofing leaves no visible traces for end users. The data packets look normal – and many systems treat them accordingly. Without in-depth analysis or logging, it’s nearly impossible to definitively identify or document an attack.
This makes IP spoofing not only effective but also ideal for long-term, inconspicuous attacks, such as preparing for future data breaches, ransomware installations, or industrial espionage.
How IP Spoofing Can Lead to False Attribution
Reversal of blame through falsified sender addresses
A particularly insidious aspect of IP spoofing is that the actual source of the attack remains invisible, as the packets appear to originate from a different device. This not only complicates forensic investigations but can also lead to the wrongful classification of innocent systems or companies as attackers, with potential consequences such as:
- Reputational damage
- legal conflicts
- Exclusion from networks
In some cases, systems can even unintentionally become part of an attack – for example, in so-called amplification attacks, where they are misused as amplifiers for DDoS waves.
Conclusion
IP spoofing is a network-level technique that attackers use to disguise the source of data packets and exploit trust between systems. It can contribute to DDoS attacks, bypass weak IP-based security controls, and complicate threat investigations. Organisations should use proper packet filtering, network segmentation, secure authentication, and continuous network monitoring to reduce these risks. Understanding how IP spoofing works is an important step toward strengthening network security.
Also Read: Best Ways To Defend Against Cyber Attack